Seminar Transcript | Tech-Law Salon: What Lawyers Should Understand About Technology-Assisted Investigative Methods
Last edited: 2026-08-30
In September 2020, the Ministry of Justice released a draft Technology-Assisted Investigation Act that would regulate investigative techniques including GPS tracking, device-side communications interception, and remote searches. The proposal attracted immediate attention. How should society balance technological capability, crime prevention and investigation, and the protection of human rights? That is an important question for contemporary civil society.
To promote discussion of that question, the Judicial Reform Foundation organized the Tech-Law Salon online lecture series and related events, inviting experts and practitioners from law and technology to discuss how investigative practices should respond to technological change and what cybersecurity safeguards must accompany that response.
Faced with an expanding range of technology-assisted investigative techniques in an increasingly complex criminal-investigation environment, how should attorneys respond, and what analytical framework should they use?
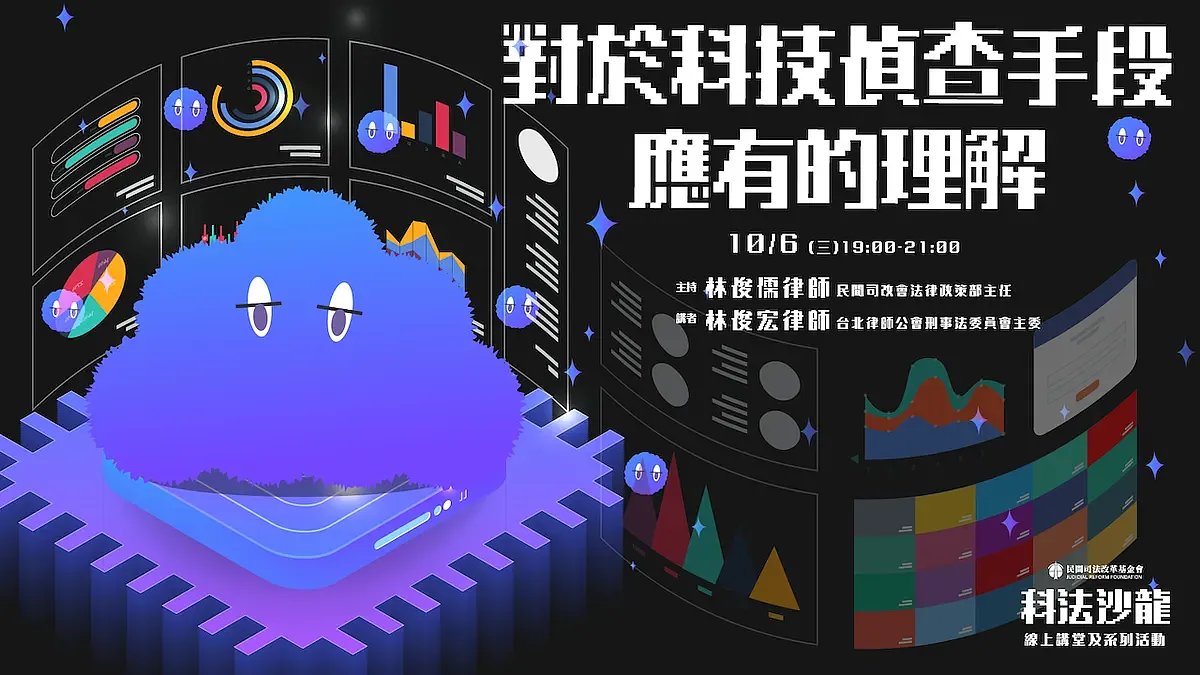
For the first Tech-Law Salon session, Attorney Lin Chun-Hung, Chair of the Taipei Bar Association Criminal Law Committee and an experienced criminal-law practitioner, introduced current technology-assisted investigation practices in Taiwan, identified problems from a defense attorney's perspective, and discussed possible responses.
▮ Time: October 6, 2021 (Wed.), 19:00-21:00
▮ Moderator: Attorney Lin Chun-Ju / Director, Legal Policy Department, Judicial Reform Foundation
▮ Speaker: Attorney Lin Chun-Hung / Chair, Criminal Law Committee, Taipei Bar Association
Seminar Transcript
Attorney Lin Chun-Ju
Welcome to the JRF's Tech-Law Salon. Let me begin by explaining why we created this series. Over the coming months, we will examine different dimensions of the Technology-Assisted Investigation Act and related policy questions. For this first session, Attorney Lin Chun-Hung will discuss what lawyers need to understand about technology-assisted investigative methods in practice.
The JRF has worked on this issue for some time because technology-assisted investigation cannot be separated from cybersecurity readiness and public cybersecurity awareness. The Tech-Law Salon is intended as a platform for broader social dialogue. Attorney Lin Chun-Hung is opening the series tonight; we plan one session each month, with Attorney Wang Wei-Hua in November, further sessions in December and January, and a concluding discussion in January.
The Ministry of Justice introduced its draft Technology-Assisted Investigation Act last year. The proposal immediately raised basic design questions. Should the law impose different safeguards in private and non-private spaces? Is it reasonable to permit GPS tracking for as long as two months at a time when, according to information we have gathered from police practice, a month is often more than enough to map a person's movements? A person's behavioral profile can emerge very quickly. Our civil-society working group has therefore been revising definitions and considering not only individual techniques but also cumulative effects: what happens when several investigative tools are used together, or when surveillance continues for a longer period? We are developing a civil-society draft with those interactions in mind and have sought input from experts and scholars throughout the process.
Tonight's subject is how technology-assisted investigative methods should be understood. For lawyers and others concerned with this issue, we want first to ask how these techniques should be analyzed through criminal procedure. But this is also a policy question: what direction should the state take? During the Q&A, we will broaden the discussion to policing policy, the digital environment, cybersecurity preparedness, and the institutional conditions needed to make that environment safer.
Attorney Lin Chun-Hung
Good evening. This was really meant to be a salon rather than a formal lecture-a chance to share some of the problems we encountered while studying the Technology-Assisted Investigation Act. We originally imagined an even more relaxed format; we were joking about giving everyone a bottle of wine. Since we are online, perhaps you can pour yourself a drink wherever you are and listen from a comfortable place.
In September last year, the Ministry of Justice suddenly released its draft Technology-Assisted Investigation Act. The consultation period was extremely short and caught many people off guard. The Taipei Bar Association quickly issued a statement, as did the Taichung Bar Association and several other bar associations, arguing that parts of the proposal went too far. The immediate background was a Supreme Court judgment that, unusually, expressly urged the legislature to fill a legal gap concerning investigative technology.
Taiwan is already using many technology-assisted investigative techniques: GPS trackers, cell-site simulators or mobile base-station vehicles, digital cellphone-location tools, drones, and thermal imaging. The next questions are even more intrusive: should investigators be allowed to deploy Trojan malware, remotely search computers, or intercept communications and LINE messages at the device level? Some of these techniques are reportedly already being used. The problem is that practice has moved ahead of the legal framework, leaving us without clear rules for when and how these powers may lawfully be exercised.
Technology-assisted investigation differs from traditional compulsory measures, but the starting point is the same: these are exercises of state power that restrict fundamental rights. Traditional measures such as search, seizure, and detention affect rights in relatively visible ways-personal liberty, property, and sometimes privacy. Communications interception brought privacy and the constitutional freedom of private communication to the forefront. More recently, personal-data protection, informational self-determination, and digital rights have become central. J.Y. Interpretations Nos. 603 and 689 recognize privacy and informational self-determination as constitutionally protected interests. If the state compulsorily intrudes into those interests, we should understand the act as an interference with fundamental rights.
As the intrusion becomes more serious, the legal requirements should become more demanding. Traditional compulsory measures generally rest on judicial authorization, sufficient suspicion, probable cause or an equivalent evidentiary threshold, and necessity. An independent judge-not the investigating officer alone-must decide whether detention, search, seizure, or another coercive measure is justified.
Communications interception shows how safeguards increase with intrusiveness. It is still a compulsory measure, but the law ordinarily demands more: judicial authorization, sufficient suspicion, necessity, limitation to specified serious offenses, particularity as to scope, minimization of the intrusion, supervision while interception is ongoing, and some form of ex post oversight. Those additional controls reflect the greater interference with privacy.
Technology-assisted investigation should be approached in the same way. Communications surveillance historically focused principally on the content of communications, even though it could also reveal metadata such as location and call duration. Newer tools can reach far more. As the amount and sensitivity of information available to the state increase, the legal safeguards should increase as well.
A Trojan or remote-search tool can potentially enter a computer and copy enormous amounts of data. If the state entered my computer, it might obtain a record of much of my past life-my daily routines, work, communications, and files accumulated over years. In some respects my devices may contain a more complete memory of me than I do myself. Allowing the state to enter those devices therefore means allowing it access to an extraordinarily detailed picture of a person.
That is why we cannot simply apply the same requirements used for traditional wiretapping. A remote intrusion may expose medical records, private photographs and videos, communications, personal interests, and other material from the core of private life. We also have to consider what happens after the state obtains the information and whether our cybersecurity environment can safely support these powers. Technical experts have described government hacking as creating an opening in the wall of a house: even after the government leaves, the vulnerability may remain. If the hole remains, someone else may be able to exploit it as well.
If the intrusion is more serious, perhaps the required level of criminal suspicion should also be higher. U.S. law, for example, uses different evidentiary standards in different contexts. Whatever terminology we use, the basic question is whether especially intrusive technology-assisted measures should require stronger factual justification than ordinary investigative steps.
The same question applies to the serious-offense requirement. Should particularly intrusive techniques be available only for offenses above a higher threshold of seriousness?
Another issue is what German law describes as technical safeguards. The technology itself may need to be designed so that investigators receive only information within the authorized scope, while irrelevant or specially protected information is filtered out. There may also need to be technical oversight of how the tool operates and of whether data are actually deleted once the authorized period ends. These safeguards matter because technology-assisted investigation is inherently difficult to contain.
I find it useful to classify current practices by how the evidence is obtained. Where investigators directly use technology against a suspect-through a cell-site simulator, drone, thermal imager, interception tool, or remote search-the compulsory nature of the measure is relatively easy to see. A harder category arises after police seize a phone or computer: may they crack the device, extract everything on it, or use its credentials to enter cloud storage? Practice often labels this "digital forensics," as though it were merely technical examination rather than a new compulsory intrusion. That classification can lower the threshold for government access even though substantial privacy interests remain at stake. A similar question arises when investigators obtain information indirectly from third parties. Communications interception is one example. Another is compelled production: a prosecutor or court asks a hospital for medical records, or another organization for records it collected for its own purposes. In practice, recipients often simply comply. But we still need to ask what kind of state power this is and what safeguards it should require.
Cloud services make that problem even more significant. Suppose investigators know that I use a Google account containing large amounts of data. May the state simply send a production order to Google and demand everything in my cloud drive? The same issue arises with domestic shopping platforms or mobility services. Gogoro, for example, may hold records capable of revealing movement patterns. Combined with purchase records and other databases, such information can reconstruct where a person goes, how long the person stays, and aspects of what the person does there.
The pandemic made this kind of data use feel unusually acceptable because digital records helped identify contacts and control infection. But that experience can normalize government access. Taiwan's contact-tracing registration data, for example, were later revealed to have been used for criminal investigations. That is exactly why we need clear rules. If these acts are compulsory measures because they interfere with protected rights, the threshold for initiating them and the procedural controls governing them should be correspondingly strict. The classification also matters later when courts decide whether evidence was lawfully obtained and may be used to determine guilt.
Technology-assisted surveillance also differs from traditional search or arrest because it is often secret. If police search your home or arrest you, you know the state has acted against you and can consider seeking a remedy. You may never know that the state has intercepted your communications, copied your computer, or assembled a detailed file tracing your life. Only later-perhaps when the information is used-might you discover how long you were monitored. In that sense, modern surveillance resembles the experience of transitional-justice victims who decades later opened state files and discovered how many people had been watching them. Technology makes the same kind of monitoring vastly easier and cheaper.
A second difference is scale. Digital collection can be indiscriminate. Investigators may need high-level access to obtain one category of information, but that access can expose everything else on the device. File names cannot reliably identify what is relevant; a private file can be labeled "draft brief" precisely so that no one else will open it. Investigators looking for evidence cannot simply trust names and may open large numbers of files. When computer data are combined with location, purchasing, medical, and other records, small pieces form a detailed portrait-the "mosaic" effect. And the intrusion does not necessarily end when collection stops. Even if officials say an irrelevant intimate file has been deleted, the person may continue wondering whether a copy remains or might leak. That continuing uncertainty is itself a significant psychological harm.
Deletion therefore cannot be treated as a purely formal promise. Digital material is easy to copy, and an affected person has little ability to verify that every copy has actually been destroyed. More broadly, I increasingly think of technology-assisted investigation as one part of the state's acquisition and use of personal information. The same structural questions arise in debates over systems such as eID: how does the state obtain information, how is it managed, who may use it, and for what purposes? It is not enough to tell people, "If you do not commit a crime, this will never affect you." Information-gathering technology can become an instrument of governance, and the law must control that power at a systemic level.
Most of the safeguards I have discussed so far are framed around technology-assisted investigation in criminal cases.
But if we step back and view state collection of personal information as a whole, the need for broader governance becomes clear. The extreme example is China's combination of facial recognition and social-credit systems. Taiwan also has the technical capacity to assemble extensive information about its population. The question is whether we should permit that. Controls therefore need to begin at the point of collection: targets and scope should be particularized, intrusions minimized, and technical safeguards required. Agencies may also need annual reporting duties, independent review, rules governing exclusion of unlawfully obtained evidence, and verifiable procedures for retention and destruction.
The same concern applies to third-party production. The Communication Security and Surveillance Act imposes cooperation duties on telecommunications providers. If future legislation imposed comparable duties on social-media and cloud platforms such as Facebook, Google, LINE, or Instagram whenever investigators claimed a crime-prevention need, the state could obtain vast amounts of information simply by sending requests. That would turn compulsory production into a substitute for investigation itself.
That brings us to a genuine dilemma. If we raise the threshold for technology-assisted investigation, one obvious safeguard is a serious-offense requirement. But strict adherence to that principle means some less serious offenses cannot be investigated with highly intrusive digital tools. That can be uncomfortable in cases such as non-consensual distribution of intimate images, which may be committed entirely through digital systems but historically have not always carried severe penalties. The choice is ultimately normative: how much investigative effectiveness are we willing to trade for stronger protection of privacy and personal data? My own view is that privacy should carry substantial weight. For the most intrusive tools, I would favor a serious-offense-or even exceptionally serious-offense-threshold. Less serious crimes should still be investigated, but with traditional or less intrusive methods. The mere fact that a technological tool is efficient does not mean the state should be allowed to use it for everything.
The second issue is particularity and specificity. A judge authorizing a measure should know exactly what method will be used, how it will operate, what information it is intended to obtain, and what its limits are. But as investigative technologies diversify, can judges realistically evaluate those technical details? I am skeptical. Even technology specialists work in highly specialized subfields. Our legal system often assumes that judicial authorization solves everything: give the issue to a judge, and the judge will protect rights. With technology-assisted investigation, however, a judge who does not understand the tool may have little practical choice but to trust the investigating agency and approve the request. Judicial authorization remains indispensable, but by itself it may not provide meaningful technical scrutiny.
A third dilemma concerns technical safeguards. German and other European approaches contemplate requirements that the technology itself be capable of limiting collection to authorized information and of restoring or securing the affected system afterward. U.S. approaches, as I understand them, are often more skeptical that such ex ante technical guarantees are realistic. Investigators may not know in advance exactly what software, exploit, or technical route will be required, so U.S. law may rely more heavily on downstream controls such as evidentiary exclusion. The underlying philosophies are quite different. If Taiwan looks to German law, technical safeguards become an important part of the discussion; if it looks elsewhere, other forms of control may be emphasized.
But the same institutional problem returns: if we require technical safeguards, can judges actually evaluate whether they are adequate? Most Taiwanese legal professionals are trained in law, not cybersecurity. And the cybersecurity issue is not abstract. If government hacking creates a vulnerability that cannot truly be closed, the state may leave a hole that others can exploit. In Taiwan, where government systems are frequent targets of foreign cyberattacks, a tool intended for criminal investigation could itself create national-security and cybersecurity risks. That is why cybersecurity preparedness has to be part of the legal design. We need technical expertise capable of asking whether the state can use these tools without leaving people exposed to malicious actors. At present, the Ministry of Justice's draft does not appear to take that problem seriously enough.
A fourth dilemma is whether Taiwan needs an independent review body. The idea arises because judicial review alone may be inadequate when judges lack the technical expertise to assess the tools before them. But what would such a body be? Another court? Something analogous to the technical examination officers used by the Intellectual Property and Commercial Court? An independent specialist agency assisting judges? Its legal status and relationship with the judiciary would have to be defined carefully. The problem becomes even harder when the state copies an entire device. Some information may fall within an inviolable core sphere of private life. Who identifies and filters that material before investigators see it? Data-protection systems such as the GDPR use institutional mechanisms including data protection officers, although in a different context. Taiwan could consider an independent review or filtering mechanism, but we do not yet have a settled model. The same issue arises with destruction: digital files are easy to duplicate, so perhaps all acquired data should pass through an independent custody system that records every access, copy, transfer, and deletion. Conceptually that is possible, but where should such an institution sit-in the Control Yuan, the National Human Rights Commission, the Executive Yuan, Academia Sinica, or somewhere else? These are difficult institutional-design questions.
A fifth dilemma is evidentiary exclusion. Once technologically obtained evidence reaches court, when should it be admissible? Material from the core sphere of private life may require absolute exclusion. What about information unrelated to the investigated offense, privileged communications, or evidence discovered incidentally? U.S. law has doctrines such as plain view; Taiwan's Code of Criminal Procedure often uses a more flexible balancing approach when evidence is unlawfully obtained. We need to decide whether technology-assisted investigation requires stronger, perhaps categorical, exclusion rules in order to deter overcollection and misuse.
A sixth dilemma is destruction. If the law requires irrelevant or expired data to be deleted, how do we verify that deletion actually occurred? Any comprehensive system for technology-assisted investigation has to answer that question.
A seventh dilemma concerns third-party cooperation. The Communication Security and Surveillance Act already imposes cooperation obligations on telecommunications providers. But future technology-assisted investigations may depend on private platforms and multinational companies that have little commercial incentive to cooperate. Consumers often choose services precisely because they believe their information will not be turned over easily to governments. During the Hong Kong anti-extradition protests, for example, people gravitated toward communications tools they perceived as safer and avoided services such as WeChat because of concern about access by Chinese authorities. Multinational companies also operate under the laws and policies of their home jurisdictions. Taiwan is a relatively small market and may have limited leverage. The legal obligations, cross-border constraints, and incentives of these third parties therefore directly affect how any technology-assisted investigation regime can work.
So my basic conclusion is that technology-assisted investigation is a form of compulsory measure, but simply invoking judicial authorization does not solve the problem. Judges remain essential, yet they may lack the specialized knowledge needed to assess complex technologies. Taiwan should therefore spend more time designing the surrounding institutions and safeguards rather than rushing to enact a Technology-Assisted Investigation Act and assuming that a judge's signature is enough. The Ministry of Justice may understandably want to place existing practices on a legal footing and make investigations easier, but the stakes are much broader. The state's use of investigative technology can weaken cybersecurity as well as privacy. If Taiwan lacks the technical environment to prevent vulnerabilities from being exploited by domestic or foreign actors, opening these powers too quickly may undermine the very security the law is supposed to protect.
An independent technical or information-review mechanism may be one promising direction. European examples, including proposals from Italy and systems in Poland, offer ideas, but no country has solved every problem. Taiwan should study comparative models without assuming it must copy one of them. It may be possible to design a better local model. The important point is that any independent body would carry substantial responsibilities-technical assessment, oversight, data handling, perhaps verification of deletion-and its design deserves serious public discussion.
Attorney Lin Chun-Ju
Thank you, Attorney Lin Chun-Hung. Listening to that overview, several points came to mind. I will briefly respond, address some of the questions you invited me to discuss, and then move into the audience Q&A.
As Attorney Lin Chun-Hung emphasized, this is not only a question of judicial authorization or the Code of Criminal Procedure. I also think about it through Science and Technology Studies (STS), which asks how technologies themselves shape politics and social relations. Facebook may know your birthday is approaching before some friends do and may predict what you want to buy. Those calculations are not merely about advertising. When similar data systems are folded into policing, they can amplify existing bias. Predictive policing and facial-recognition systems are familiar examples: historical patterns of discrimination can be encoded into algorithms and carried forward into future decisions. Technology acts like a catalyst. If we begin from the assumption that every social problem is a policing problem, technology can accelerate the consequences of that assumption. Claims of efficiency also need to be tested more broadly. GPS tracking may reduce the cost of physical surveillance, but poorly designed systems can create high litigation, compliance, and cybersecurity costs. Without adequate legal and technical infrastructure, a supposedly efficient investigative tool can impose new burdens on law enforcement and the courts.
Evidence preservation illustrates the point. Digital evidence-network packets, encrypted communications, logs-must retain integrity if it is to survive challenge in court, and reliable preservation can be expensive. We have discussed the potentially enormous cost of retaining network traffic and encrypted-system data. From an STS perspective, the real policy question therefore extends beyond criminal-procedure doctrine and judicial authorization. It includes policing policy, criminal policy, cybersecurity, and governance of the digital environment. Comparative law can help: Italian proposals concerning registration and auditability of Trojan tools, Polish reporting requirements, and other European, U.S., and German approaches all offer different mechanisms. The JRF's working group has been studying these models since last October. We welcome practitioners' experience and suggestions as we continue developing the civil-society draft.
Attorney Lin Chun-Hung
Does Taiwan need legislation governing technology-assisted investigative methods? I think the answer is yes. The need exists. The real questions are what powers should be authorized, what thresholds should apply, and how those powers should be controlled.
The Ministry of Justice's earlier draft, in my view, tried to open too much at once and left important powers buried in broad language. Remote searches are a good example: can the state infect a computer with malware and search it from afar? Some provisions appear to say no, but could be read to allow it. Other techniques, such as GPS tracking, may be easier to justify because there are real investigative needs. Even there, duration is crucial. One or two weeks of tracking may already reveal a person's routine; permitting much longer periods can produce a detailed behavioral profile that goes far beyond a single investigative objective.
Other databases make that profiling even easier. During the pandemic, systems capable of linking consumption and movement records demonstrated how separate data points can be combined. If the state knows where you travel and what you purchase, it may infer highly private patterns of life. The Ministry of Justice draft set relatively low thresholds for some of these powers because its overriding concern was to legalize existing practices and facilitate investigation. Rights protection received less weight.
The draft also did not adequately answer what happens to the information after it is obtained-how long it may be retained, who may use it, and how its destruction can be verified.
Q&A
Attorney Lin Chun-Ju
An audience member asks: these technologically enabled compulsory investigative measures extend beyond traditional criminal law and criminal procedure. Where the future Technology-Assisted Investigation Act or the Code of Criminal Procedure does not provide enough protection, can the Communication Security and Surveillance Act or the Freedom of Government Information Law be used defensively-for example, to require disclosure of how often state Trojans are used in criminal investigations each year?
A second question is whether the JRF or bar associations could establish or participate in a third-party technical-safeguard body. Attorney Lin Chun-Hung, could you address those two questions?
Attorney Lin Chun-Hung
Those are difficult questions. As the safeguards become stricter, transparency can certainly be part of the answer. Rather than relying only on individual requests under the Freedom of Government Information Law, I would prefer legislation that directly requires law-enforcement agencies to submit periodic reports to the legislature, the National Human Rights Commission, or another oversight body. The National Human Rights Commission might also be given audit authority to examine which technology-assisted investigative methods were used during the year, what categories of information were obtained, and what equipment was purchased. Comparing those records could help expose unlawful or unreported practices.
I would put those reporting duties directly into the future Technology-Assisted Investigation Act. Whenever the state uses these tools-whether under the Code of Criminal Procedure or another legal basis-it should have an affirmative obligation to report what methods were used and what information was obtained, so the public can understand the scope of the power being exercised.
As for a third-party technical role, the JRF itself is probably not suitable. Our institutional role is to supervise government, not to become part of the government's operational machinery. Bar associations may be a more plausible possibility. In earlier discussions about evidence custody, we considered whether blockchain-style systems could create decentralized, de-identified, tamper-resistant records of the chain of custody, perhaps through a permissioned network and smart contracts requiring multiple actors to validate access. A bar association or another trusted independent institution might conceivably participate in such a system. Whether government would delegate that role, whether the necessary budget and technical capacity exist, and whether the Executive Yuan would support the arrangement are separate questions. But it is a direction worth exploring.
Attorney Lin Chun-Ju
Let me continue with two more questions. The third asks whether contact-tracing registration data or GPS records can also work in the opposite direction-as evidence establishing a defendant's alibi.
The fourth asks whether an independent review body could conduct ex ante review, prevent abuse, trace later leaks, and verify destruction of information, thereby better balancing investigative needs with individual rights. What kinds of independent supervisory mechanisms exist abroad?
Attorney Lin Chun-Hung
On the third question, of course the data can be used defensively if they exist. But that is a double-edged sword. Do we want the state to monitor everyone's location and communications continuously on the theory that the records might someday prove an alibi? I do not accept that logic. If a person wants to preserve personal location history, current technology already allows that-for example, through a private Google location-history setting. The individual can choose to collect and store those records and produce them later if needed. I would rather control my own data than have the state collect it for me and risk misuse.
For the fourth question, I will defer to Attorney Lin Chun-Ju, who has studied the comparative models in more detail.
Attorney Lin Chun-Ju
I will ask Attorney Lin Chun-Hung to return to the question of legislative necessity and policy choices afterward. Let me first address the transparency and oversight questions. When the JRF studied comparative law for the civil-society draft, we looked at systems that require periodic public reporting. The discussion included provisions in Polish police law and the German Code of Criminal Procedure requiring annual reports with detailed information such as the number of technology-assisted compulsory measures used and the types of offenses involved. We think that kind of disclosure is a useful model and hope to incorporate comparable reporting into the civil-society proposal.
Existing rules under the Communication Security and Surveillance Act and the proposed Technology-Assisted Investigation Act provide some degree of disclosure, but effective reporting also requires the reporting authority to obtain usage logs and activity data from the agencies actually deploying the tools. We therefore considered provisions preventing those agencies from refusing to provide the necessary data to the Ministry of Justice. The remaining question is how broad the reporting obligation should be: reports to the legislature, full online disclosure to the public, or some combination. Civil society is still discussing the appropriate model.
The fourth question is whether Taiwan should establish an independent review body. At a Legislative Yuan Judiciary and Organic Laws and Statutes Committee hearing last October, the JRF and other civil-society organizations raised a more basic institutional problem: Taiwan still lacked a fully developed dedicated data-protection authority. If the country has not yet built that foundation, designing a specialized independent body for technology-assisted criminal investigation may be getting ahead of ourselves. Still, comparative systems offer several possible approaches-specialized oversight, technical capacity-building within government, and institutional arrangements that combine legal and technical expertise. I can only sketch those models here; the details would require closer study of each jurisdiction's current system.
One approach is comprehensive logging of how investigative technology is used. German rules, for example, require records concerning the tools deployed, the implementing agency, dates of use, and resulting information. That makes later oversight more concrete. An especially interesting Italian proposal from 2017 would have created a Trojan-program registry tracking the production and use of government hacking tools, preserving fingerprints for each software version, and placing source code and original files with a designated institution for reproducible verification. Technical experts have told us that detailed logging could serve a similar function. The proposal also contemplated periodic review so that legal and technical standards could keep pace with changing technology. The 2017 Italian proposal did not ultimately pass, but the institutional idea is worth studying.
Another approach is to strengthen independent supervision through judicial or human-rights institutions. The United Kingdom's Investigatory Powers Act, for example, operates alongside mechanisms including the Investigatory Powers Commissioner and the independent Investigatory Powers Tribunal. The Commissioner performs oversight of the use of investigatory powers, while the Tribunal hears relevant complaints and disputes. The broader lesson is that foreign systems do not rely on a single institutional form: some emphasize specialized judicial scrutiny, some recordkeeping and audits, and some separate complaint mechanisms. Taiwan currently lacks a comparably developed oversight structure, so these models remain useful starting points even if they have not yet been translated into a concrete domestic proposal.
Attorney Lin Chun-Hung
We previously considered whether the National Human Rights Commission might play some role. Because that would implicate Taiwan's constitutional and institutional structure, any such design would require a clear legal basis, defined powers, and adequate resources. More importantly, creating an independent review body does not automatically solve the problem. Its relationship with judges-who decides what, and with what degree of authority-would still have to be worked out carefully.
At an even broader level, Taiwan needs a coherent framework for how the state acquires, uses, and protects personal information. That question is larger and more complicated than criminal investigation alone, but it cannot be avoided. We should not remain in a position where the competent authority itself is unclear.
Attorney Lin Chun-Ju
While we wait for further questions, let me summarize another way of framing the problem that technical experts have suggested to us. Think of the policy in three layers. The first is cross-border data governance: rules resembling private international law, the U.S. CLOUD Act, and other mechanisms governing cross-border requests and transfers. Those questions inevitably involve international bargaining power, which is very different for the United States and for Taiwan. The second layer is cybersecurity infrastructure. The third is criminal investigation itself. Even within criminal investigation, proportionality matters: a powerful hacking tool might conceivably be justified against organized crime or serious external threats, but not merely because someone sold a few grams of cannabis. The seriousness and nature of the offense must matter.
Seen through those three layers-cross-border legal arrangements, cybersecurity infrastructure, and criminal investigation-the policy problem becomes much broader than a single criminal-procedure statute.
A common analogy is that giving government powerful surveillance capability is like putting a gun to someone's head and saying, "Trust me, I will not pull the trigger." But the person who eventually pulls the trigger may not even be the Taiwan government. A vulnerability left by an investigative tool can be exploited by outside actors through data leaks or undiscovered security flaws. Because these tools can be difficult to remove cleanly, poorly designed systems may expose Taiwanese citizens to greater cybersecurity risk while also imposing heavy burdens on police and courts. Comparative studies from the United States and European Union therefore stress supporting measures such as secure encryption, privacy-impact assessments, particularized warrants, clear statutory authority, training, operational manuals, and reliable procedures for removing or disabling the relevant hardware and software. Without that infrastructure, legislation may create enormous costs without achieving its stated investigative goals. The JRF wants to discuss those policy layers together with the criminal-procedure dilemmas Attorney Lin Chun-Hung identified, and we continue to invite lawyers and other specialists to participate in the working group.
Attorney Lin Chun-Hung
Let me add one point about cybersecurity. Technology-assisted investigative methods do not merely intrude on personal information; they can weaken the security architecture protecting that information. We also have to ask whether government agencies themselves have sufficient cybersecurity capacity. Threats are not only domestic. If the state collects large quantities of personal data and stores them in government clouds or centralized repositories without adequate protection, it may effectively gather the information in one convenient place for foreign or malicious actors to attack.
I cannot say with certainty whether Taiwan's current cybersecurity environment is adequate. But technical experts we consulted were not especially reassuring. If the government wants authority to collect far more personal information, it must also be able to protect that information. If it cannot confidently do so, on what basis should it be trusted with such extensive access? Otherwise the state may simply collect and organize data for someone else to steal.
Rushing to enact a law before those foundational security questions are answered is, in my view, irresponsible. Before the state acquires sweeping new powers because it says investigation requires them, Taiwan should first determine whether it has the institutional and technical capacity to use those powers safely. Based on the experts we have consulted, significant improvement is still needed.
Attorney Lin Chun-Ju
Thank you, Attorney Lin Chun-Hung. Cybersecurity preparedness has been a major part of the JRF's own work on this draft, and technical specialists have contributed important perspectives. We want the public dialogue to go beyond the Code of Criminal Procedure and police powers and address the condition of the entire cybersecurity environment. Once the speakers are confirmed, we will announce the November, December, and January sessions on the JRF website. We will also continue dialogue with the technical community, including work connected with the Taiwan Internet Governance Forum, and publish related materials online. Anyone interested is welcome to follow the series or join our working-group discussions. Since there do not appear to be additional questions, Attorney Lin Chun-Hung, do you have any closing thoughts?
Attorney Lin Chun-Hung
The purpose of the Tech-Law Salon is to create a platform for dialogue. This first session was simply an invitation to begin thinking about technology-assisted investigation, because these powers can affect everyone even though many people rarely stop to consider them. We hope the salon generates broader discussion and attention. This is our first attempt, so if you have suggestions about the format, please tell us and we will adjust.
The conversation should include lawyers, non-lawyers, technologists, and other stakeholders who see the issue from different angles. Regulation of technology-assisted investigation is still evolving around the world; Taiwan does not have to copy either the U.S. or German model. Perhaps we can develop a Taiwan model that others eventually find useful. What matters is sustained dialogue and a willingness to improve the framework as technology and practice change.
Tonight may have felt a little more formal than I originally imagined. I had hoped for something very relaxed, because people often talk more freely that way. But the important thing is that the conversation continues. Perhaps next time, when in-person gatherings are possible, we can sit together over coffee or a drink and have an even better exchange. Please keep sending us your ideas.
Attorney Lin Chun-Ju
Thank you, Attorney Lin Chun-Hung. At the heart of this discussion are digital human rights. German law speaks of informational self-determination and the core sphere of private life. When separate pieces of information are assembled into a "mosaic," the resulting portrait can itself implicate human dignity. If the state can reconstruct who you are, how you live, and the course of your life, genuine freedom becomes harder. People need spaces in which they are not being watched so they can explore boundaries, ideas, and ways of living. Human rights must preserve that space.
The Tech-Law Salon is one starting point for that broader conversation. We are grateful to Attorney Lin Chun-Hung for opening the series and for discussing both the proper understanding of technology-assisted investigative methods and the comparative-law questions raised by the draft.
For the next session in November, we will invite Attorney Wang Wei-Hua to examine investigative law and policy from a U.S.-law perspective. We will announce the details on the JRF website and Facebook. We also welcome suggestions about the salon itself. Anyone interested in joining the policy working group may email our staff; we will send information about the next meeting so that participants can join the discussion online. Our goal is to make Taiwan's digital environment more reasonable, meet legitimate investigative needs, and protect individual rights at the same time.
That is what we most hope the Tech-Law Salon can accomplish. Thank you all for participating, and thank you to Attorney Lin Chun-Hung and everyone still listening online. We will end here. See you next time.
Attachment
Lin Chun-Hung / Presentation: Proper Understandings of Technology-Assisted Investigative Methods
This article is an AI-generated translation of the original Chinese text. In the event of any discrepancy, the Chinese version shall prevail.